Why we exist

Technology risk is hard to explain and easy to underestimate. Boards want a straight answer. Technical teams want a fair reading of what they've built. Too often, neither gets one.

We start­ed CyberVerge Advisory to give both. We pair hands-on tech­ni­cal knowl­edge with a work­ing com­mand of com­pli­ance re­quire­ments, so our find­ings stay ac­cu­rate and our ad­vice stays us­able.

What we do

CyberVerge Advisory LLC de­liv­ers fo­cused ad­vi­so­ry in IT audit con­sult­ing; AI audit and gov­er­nance; gov­er­nance, risk, and com­pli­ance (GRC); and pro­fes­sion­al train­ing.

We help lead­ers strength­en con­trol en­vi­ron­ments, man­age risk, and build re­silient frame­works aligned to busi­ness goals. Boards, ex­ec­u­tives, and risk lead­ers come to us when tech­nol­o­gy and reg­u­la­to­ry pres­sure start to pile up. We turn that pres­sure into clear, ac­tion­able guid­ance.

Our mission

To make technology risk understandable and manageable for the people accountable for it.

How we think

Controls come first

Tools change every year. Sound controls change slowly. We build advice around the second, so it keeps working when the first changes.

Clear beats clever

A finding nobody understands doesn't reduce risk. We write for the person who has to act on it.

Fit matters

We study how leading professional services firms approach risk, then adapt the practices that suit your size and budget. You won't get a template built for someone else.

Evidence over opinion

Our conclusions rest on what we observe and test. We show our work, so you can challenge it.

What makes our approach different

Every risk we raise connects to a control, an owner, and an action. Generic recommendations can't pass that test, so you won't receive any.

We also stay lean. Engagements are personal and scoped to your needs. You don't wait for a large firm's staffing cycle, and you don't pay for layers you didn't ask for.

Our commitments to you

  1. A written scope before work begins, with deliverables, timing, and fees.

  2. Reports in plain language, with a short summary for leaders.

  3. Confidential handling of everything you share, under a signed NDA when you want one.

  4. Honest answers, including when we aren't the right fit.

Who we work with

Mid-market and enterprise organizations across industries.

Our clients want in­de­pen­dent-mind­ed ad­vice, bet­ter vis­i­bil­i­ty into risk, and frame­works built for the way they use tech­nol­o­gy today. They in­clude boards and audit com­mit­tees, tech­nol­o­gy and se­cu­ri­ty lead­ers, risk and com­pli­ance teams, and in­ter­nal audit func­tions that need added ca­pac­i­ty or spe­cial­ist depth.

Where our work starts and stops

CyberVerge Advisory LLC is not a CPA firm. We don't per­form fi­nan­cial state­ment au­dits, issue audit opin­ions, or pro­vide at­test ser­vices. We don't give legal ad­vice, and we don't cer­ti­fy com­pli­ance.

We ad­vise, as­sess, and train. When your sit­u­a­tion calls for a li­censed CPA firm or legal coun­sel, we'll say so plain­ly and work along­side them.

Frameworks we work with

We map our work to standards your regulators, customers, and boards already recognize.

Cybersecurity and IT controls

  • NIST Cybersecurity Framework 2.0
  • NIST SP 800-53
  • ISO/IEC 27001
  • ISO/IEC 27002
  • CIS Controls
  • COBIT

Privacy

  • ISO/IEC 27701
  • NIST Privacy Framework

AI governance

  • NIST AI Risk Management Framework
  • ISO/IEC 42001
  • ISO/IEC 23894
  • EU AI Act

Risk, resilience, and internal control

  • COSO Internal Control
  • COSO ERM
  • ISO 31000
  • ISO 22301

Reporting and industry requirements

  • SOC 2 (AICPA Trust Services Criteria)
  • PCI DSS
  • HIPAA Security Rule

Our values

Objectivity

Our findings follow the evidence, whoever it surprises.

Clarity

We say what we found, what it means, and what to do next.

Practicality

Advice you can budget, schedule, and finish.

Integrity

We tell you when a job isn't ours to do.

Leadership

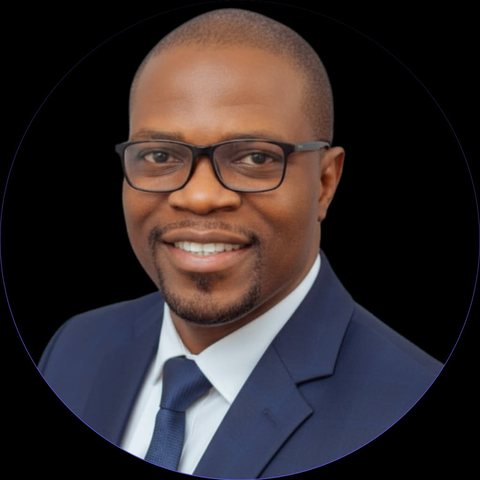
Portrait of Dr. Nath Alagbe

Dr. Nath Alagbe

Principal Advisor

Dr. Nath Alagbe is the founder and Principal Advisor of CyberVerge Advisory LLC. He brings more than 12 years in the U.S. fi­nan­cial ser­vices in­dus­try and sub­ject-mat­ter ex­per­tise across every ser­vice the firm of­fers, from IT audit and cy­ber­se­cu­ri­ty to AI risk, pri­va­cy, and foren­sic ac­count­ing. He found­ed the firm on a sim­ple be­lief: lead­ers make bet­ter de­ci­sions when tech­nol­o­gy risk is ex­plained in plain lan­guage and tied to ac­tion.

Meet the Full Team

Want to see if we're a fit?

A short conversation is the fastest way to find out.